Key Takeaways
- Generative AI has created a new security boundary across prompts, files, models, and AI-powered workplace tools.
- Sensitive data is contextual, making pattern-based DLP insufficient for many AI interactions.
- Enterprises need visibility and control across every AI interaction, including shadow AI.
- The goal isn’t to stop AI adoption, but to make AI use safe without sacrificing productivity.
An executive whitepaper on how AI-Native DLP differs from legacy DLP, and what it means for enterprise security strategy.
Download WhitepaperGenerative AI is already embedded in how enterprises work.
Employees use ChatGPT to analyze reports, Claude to summarize documents, Gemini to draft emails, Copilot to write code, and AI tools inside Slack, Notion, Microsoft 365, and other workplace applications.
The problem is not whether employees are using AI. They already are.
The problem is knowing what data is being shared, where it is going, what the AI is doing with it, and whether your security controls can understand the context.
Every prompt creates a potential data exposure. Every AI-generated output can introduce risk. And every unsanctioned AI tool creates another blind spot for security teams.
This is a fundamentally different security problem.
Traditional security controls were built around networks, endpoints, applications, files, and known data patterns. Generative AI introduces an attack surface that lives in language, context, prompts, models, and interactions.
You cannot secure that attack surface by simply blocking ports or scanning binaries.
You need to understand what is being said.
What Is Generative AI Security?
Generative AI security is the practice of protecting AI systems, the data they process, and the people using them from security, privacy, compliance, and operational risks.
It spans the entire AI lifecycle, from model development and training to deployment, inference, and everyday employee interactions.
For enterprises, that means protecting against threats such as:
- Sensitive data leakage
- Prompt injection
- Shadow AI
- Data poisoning
- Model and supply-chain attacks
- Insecure AI-generated code
- Unauthorized access and misuse
- Compliance and privacy violations
- Hallucinations and unreliable outputs
But there is an important distinction.
Not every AI security problem occurs inside the model or infrastructure.
A significant part of the risk begins before the prompt even reaches the model.
An employee can paste customer information into ChatGPT. A developer can send proprietary source code to an AI coding assistant. A finance employee can upload an internal forecast to summarize it.
The model may work exactly as designed.
The security failure happened when sensitive information left the organization’s control.
Why Generative AI Creates a New Security Attack Surface
AI changes the nature of the data security problem.
A traditional application might process structured fields, files, database records, or network traffic. Generative AI processes natural language and unstructured information.
That makes context critical.
Consider these two prompts:
“Customer: Acme Corp, Contract Value: $4.2M”
and:
“Summarize the renewal strategy for our largest healthcare customer in California.”
The second prompt may contain commercially sensitive information even though it contains no obvious PII, credit card number, or keyword that a traditional DLP rule would recognize.
This is where conventional controls begin to struggle.
The risk is no longer just what the data looks like. It’s what the data means.
The Biggest Generative AI Security Risks
1. Sensitive Data Leakage
Employees can unintentionally expose PII, PHI, financial information, source code, customer information, intellectual property, or confidential business strategy through AI prompts.
The challenge is that sensitive information isn’t always formatted like sensitive information.
A customer can be described without their name. A confidential project can be referenced without using the project’s codename. A trade secret can be embedded inside an otherwise ordinary paragraph.
Security controls need to understand the context, not just search for patterns.
2. Shadow AI
Employees don’t wait for IT to approve every productivity tool.
They use whatever helps them get their work done.
That creates shadow AI: unsanctioned AI tools being used without security approval, centralized policies, or adequate visibility.
For security teams, this creates three problems:
No visibility. No control. No reliable audit trail.
Blocking every public AI tool isn’t a realistic answer either. Employees will find alternatives, often creating even larger blind spots.
The better approach is to give employees access to AI while controlling how enterprise data moves into those systems.
3. Prompt Injection
Prompt injection attacks manipulate an AI model through carefully crafted instructions.
An attacker might attempt to override system instructions, extract sensitive information, manipulate an AI agent, or cause it to perform an unintended action.
As enterprises move from simple chatbots toward AI agents that can access files, applications, and business systems, the potential impact becomes significantly greater.
4. Data Poisoning
AI systems depend on data.
If training, fine-tuning, feedback, or retrieval data is manipulated, attackers may influence model behavior or introduce vulnerabilities that are difficult to detect.
The larger and more complex the AI ecosystem becomes, the harder it is to establish complete trust in every dataset and dependency.
5. Model Theft and Supply-Chain Risk
Organizations increasingly depend on third-party models, APIs, plugins, datasets, and AI infrastructure.
That expands the supply chain.
Attackers can target model endpoints, attempt to extract model behavior, compromise dependencies, or exploit weaknesses in third-party AI services.
AI security therefore cannot stop at the organization’s own infrastructure. Security teams need visibility into the broader AI stack.
6. AI-Generated Code Vulnerabilities
AI coding assistants can dramatically accelerate development.
They can also generate insecure code.
Developers may unknowingly introduce vulnerabilities, outdated dependencies, improper authentication, or other security flaws into production systems.
AI-assisted development needs the same security discipline as any other software development process, with additional controls around how proprietary code and context are shared with external models.
7. Hallucinations, Bias, and Unreliable Outputs
Not every AI risk is an attack.
Models can produce incorrect, fabricated, or biased outputs without being compromised.
When AI is used for customer communications, financial analysis, healthcare, legal work, or other high-impact decisions, unreliable output can become a compliance, operational, and reputational risk.
Security and governance therefore need to account for both malicious behavior and unintended model behavior.
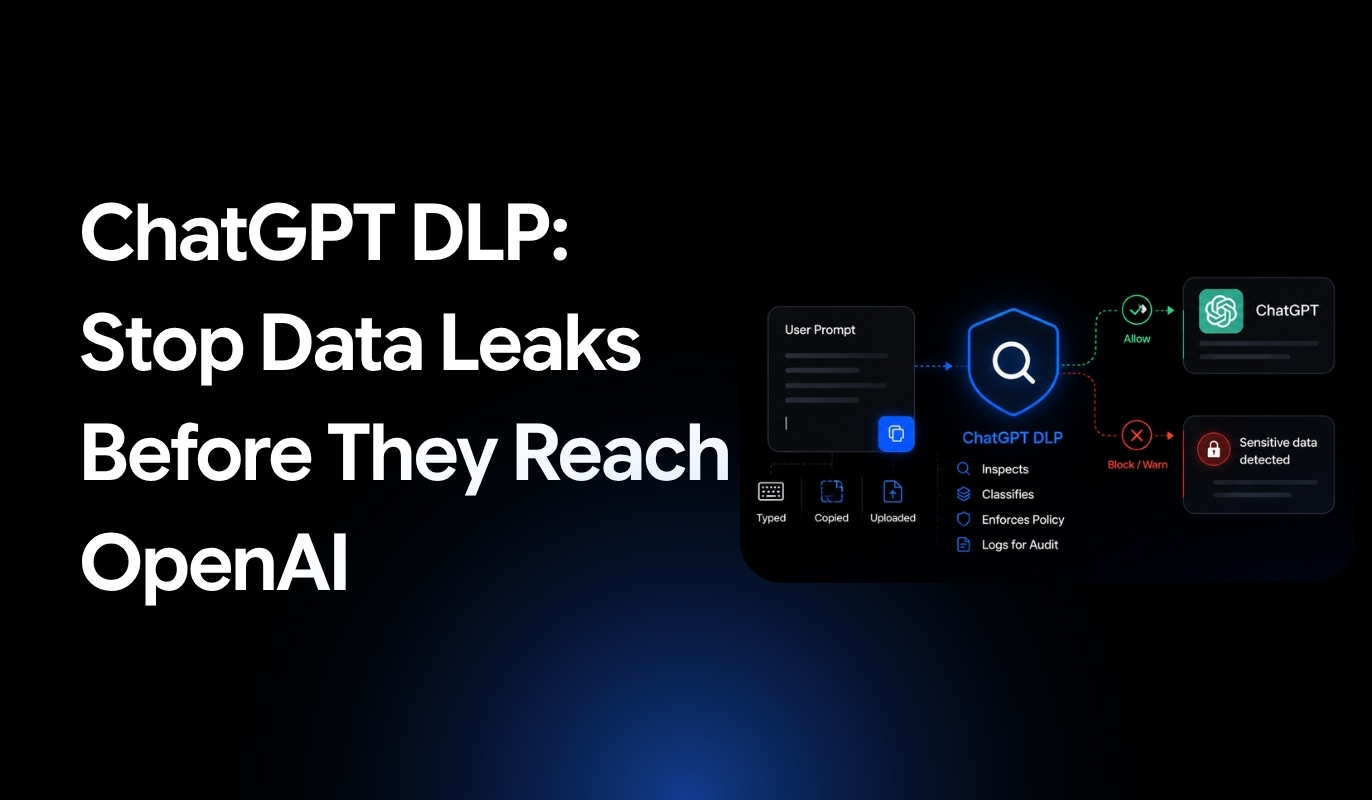
Why Traditional DLP Falls Short for Generative AI
Traditional Data Loss Prevention was largely designed to identify known sensitive information.
Credit card numbers. Social security numbers. Email addresses. File patterns. Keywords.
These controls remain useful.
But generative AI introduces a different problem: semantic exposure.
Imagine an employee writes:
“Write a summary of the acquisition we’re planning for the company we met at the healthcare conference last month.”
There may be no obvious PII pattern to detect.
Yet the prompt could reveal a confidential acquisition target.
A regex cannot understand that.
A keyword rule cannot understand that.
A context-aware security system can.
This is the shift from pattern-based DLP to contextual DLP.
Traditional DLP asks:
“Does this text contain a known sensitive pattern?”
AI-aware DLP needs to ask:
“What does this information mean in this interaction, and should it be allowed to reach this model?”
That distinction becomes critical as AI adoption scales.
What a Modern Generative AI Security Framework Looks Like
Securing enterprise AI requires controls across several layers.
Data Protection
Sensitive data should be identified, classified, masked, tokenized, or encrypted before it reaches AI systems.
Access Control
Organizations need to determine who can use which AI models, applications, agents, and capabilities.
Input and Output Security
Prompts and responses should be evaluated for sensitive information, malicious instructions, policy violations, and other risks in real time.
Infrastructure Security
AI workloads should follow established security principles such as least privilege, workload isolation, network segmentation, and continuous monitoring.
Model Governance
Organizations need visibility into model lineage, versions, datasets, changes, and behavior over time.
Adversarial Testing
Security teams should test AI applications against prompt injection, data poisoning, jailbreaks, data leakage, and other attack techniques before deployment.
Monitoring and Auditability
AI usage needs to be observable.
Security teams should know which users are interacting with which AI systems, what policies were triggered, what data was blocked or redacted, and where anomalous behavior is occurring.
This broader approach aligns with frameworks such as Gartner’s AI TRiSM model, which emphasizes trust, risk, and security management throughout the AI lifecycle.
Best Practices for Enterprise Gen AI Security
Organizations adopting generative AI should start with a few practical controls.
1. Build an AI inventory.
Know which models, APIs, applications, agents, datasets, and AI-powered workplace tools your employees are using.
2. Establish an AI usage policy.
Define what employees can and cannot share with AI systems, and make those policies enforceable rather than purely educational.
3. Protect sensitive data before inference.
Use encryption, tokenization, masking, and contextual redaction to prevent sensitive information from leaving the organization’s control.
4. Apply zero-trust principles.
Limit access based on identity, role, application, model, and business context.
5. Monitor shadow AI.
Visibility should extend beyond sanctioned applications to the AI tools employees actually use.
6. Test for adversarial behavior.
Regularly evaluate AI applications for prompt injection, jailbreaks, data leakage, and other attack paths.
7. Maintain model and data lineage.
Know where models and datasets came from, how they changed, and what dependencies they rely on.
8. Prepare incident response plans.
AI incidents require dedicated playbooks for data leakage, compromised models, malicious prompts, anomalous outputs, and unauthorized AI usage.
9. Train employees.
Employees remain part of the security boundary. They need clear guidance on what information should never be entered into public AI systems.
Securing the AI Conversation Layer With Wald
Most enterprise AI interactions begin with a conversation.
A prompt is written. Context is added. Files are attached. Information is sent to a model. A response comes back.
That interaction is a security boundary.
Wald secures that boundary with Context Intelligence.
Instead of relying solely on predefined patterns, Wald analyzes the meaning and context of AI interactions to identify sensitive information before it reaches the model.
For example, consider:
“Our biggest healthcare customer in California is considering a $10M expansion.”
There may be no name, account number, or obvious PII to detect.
But the statement can still reveal confidential business information.
Wald’s contextual approach can identify the sensitivity of that information and apply the organization’s policy in real time.
Context-aware redaction
Wald evaluates information based on meaning and context, helping detect sensitive information that traditional pattern-based DLP can miss.
Inline protection
Policies are enforced during the AI interaction rather than relying solely on after-the-fact monitoring.
Visibility across AI usage
Security teams can gain visibility into interactions across AI systems such as ChatGPT, Claude, Gemini, and Llama, including usage that may otherwise fall into the shadow AI gap.
Enterprise governance
Organizations can establish policies around how employees interact with AI while maintaining the productivity benefits that drove adoption in the first place.
The goal isn’t to stop employees from using AI.
It’s to make enterprise AI use safe enough to say yes to.
Is Generative AI Security Actually Possible?
Perfect security isn’t realistic.
AI systems are complex. Attackers adapt. Models behave probabilistically. Employees will continue experimenting with new tools.
But that doesn’t mean organizations have to accept uncontrolled exposure.
The objective is resilience.
Enterprises can reduce risk by combining governance, visibility, access controls, adversarial testing, and data protection with security controls that understand the unique nature of AI interactions.
The key shift is simple:
Don’t treat AI as just another application.
Treat it as a new security boundary.
The Next Step for Security Leaders
Generative AI adoption is moving faster than traditional security processes were designed to handle.
The question for CISOs is no longer whether employees will use AI.
They will.
The question is whether security teams can give employees the freedom to use it without giving sensitive enterprise data away with every prompt.
That requires visibility into AI usage, enforceable policies, and security controls that understand context rather than simply matching patterns.
Wald provides that contextual security layer between your employees and the AI systems they use, helping organizations adopt generative AI without losing control of their data.