Grok DLP for the Way Employees Actually Use AI
Prevent sensitive data leaks with contextual AI that understands prompts, coaches users in real time, and enforces policies before data reaches Grok.
Book A Demo
Maintains compliance with:
Risks in using Grok
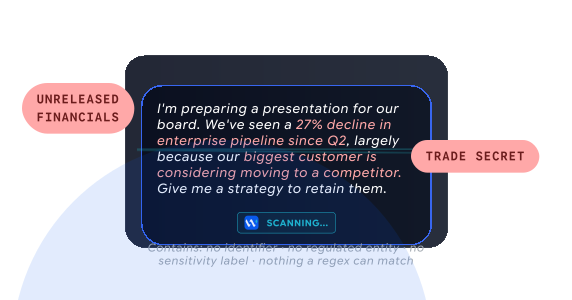
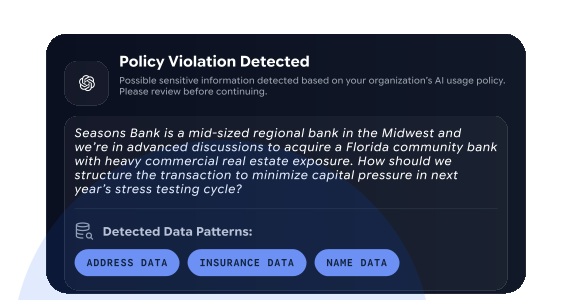
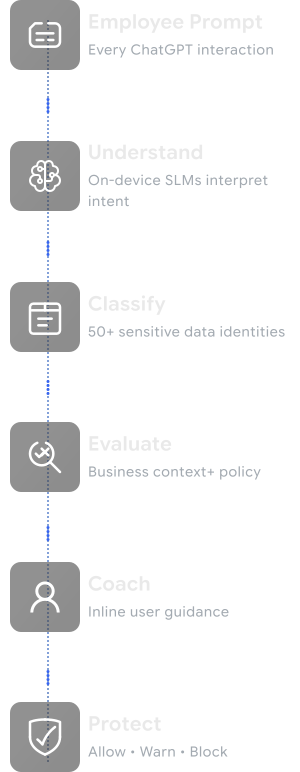
Understand every Grok prompt
On-device SLMs classify prompt context before sensitive data reaches Grok.
- 50+ data identities
- Semantic understanding
- Inline user coaching
Protect every Grok interaction
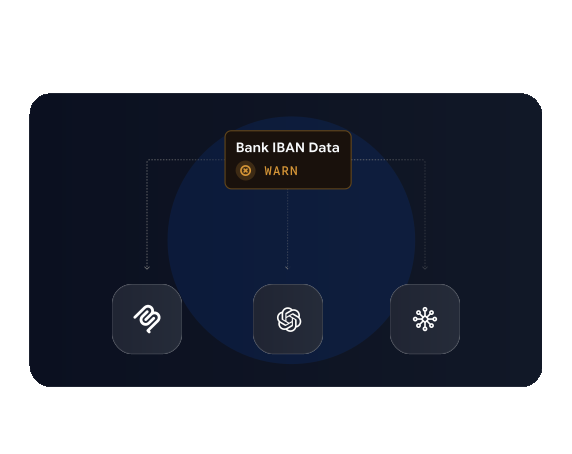
Enforce Allow, Warn, Block, or Redact policies before sensitive data reaches Grok.
- Real-time policy enforcement
- Prompt & response protection
- Browser & desktop coverage
Scale beyond Grok
Apply the same protection across Grok, AI agents, and MCP servers through a unified policy engine.
- AI agents & MCP servers
- Centralized audit trail
- Dynamic AI policies
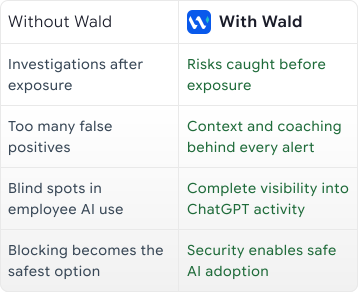
What changes for you?
Why Context Beats Keywords
Legacy DLP looks for keywords and patterns. Wald's on-device SLMs understand the intent and business context behind every Grok prompt, enabling accurate policy decisions before sensitive data reaches AI.
Frequently Asked Questions
Contact UsWhat does Grok DLP protect against?
Wald’s Grok DLP helps prevent employees from sending sensitive or confidential information into AI interactions. That can include PII, financial information, source code, credentials, proprietary business information, and other sensitive data. OWASP identifies sensitive information disclosure as a key risk in LLM applications, including exposure of PII, financial data, confidential business information, credentials, and legal documents.
Wald adds an inline control layer that evaluates the interaction before sensitive data reaches Grok, allowing organizations to allow, warn, block, or redact based on their policies.
Why do I need DLP if my organization already uses Grok Business or Enterprise?
Grok Business and Grok Enterprise provide important workspace-level privacy and administrative controls. xAI states that business data is not used to train its models, and administrators can manage users, access, and usage from the xAI console, with SSO and advanced audit controls on the Enterprise tier.
Those controls address how the Grok workspace is managed. Wald addresses what employees actually put into AI interactions, applying contextual DLP policies before sensitive information is shared, including when employees reach Grok through personal accounts or inside X.
Can Grok DLP distinguish between legitimate AI use and risky data sharing?
Yes. The key is evaluating the context of the interaction, rather than relying only on recognizable sensitive-data patterns.
Wald's on-device SLM evaluates the prompt context and sensitive data together, helping security teams distinguish legitimate AI-assisted work from interactions that create a data-exposure risk.This is important because sensitive information can be disclosed through ordinary-looking AI interactions, not only through obvious credentials or PII patterns.
Does Wald only protect Grok?
No. Grok can be one part of a much larger AI environment. Wald extends its protection across AI applications, browsers, desktops, AI agents, and MCP servers, using a unified policy approach.
This becomes increasingly relevant as organizations adopt AI agents and connected AI apps that can access company systems. Grok Business, for example, lets users connect company tools such as Google Drive and share conversations with teammates, which widens the paths sensitive data can travel.
Does Grok DLP block employees from using AI?
It doesn't have to. The goal is to enable safe AI use rather than default to blocking it.Wald can apply different actions based on the context and policy: Allow, Warn, Block, or Redact. This lets organizations protect sensitive information while allowing employees to continue using AI for legitimate work.
How is Wald different from traditional DLP?
Traditional DLP is generally built around identifying known data patterns and applying predefined rules. Wald adds contextual understanding to AI interactions, helping determine what the user is asking AI to do with the data, not just whether a recognizable sensitive-data pattern appears.